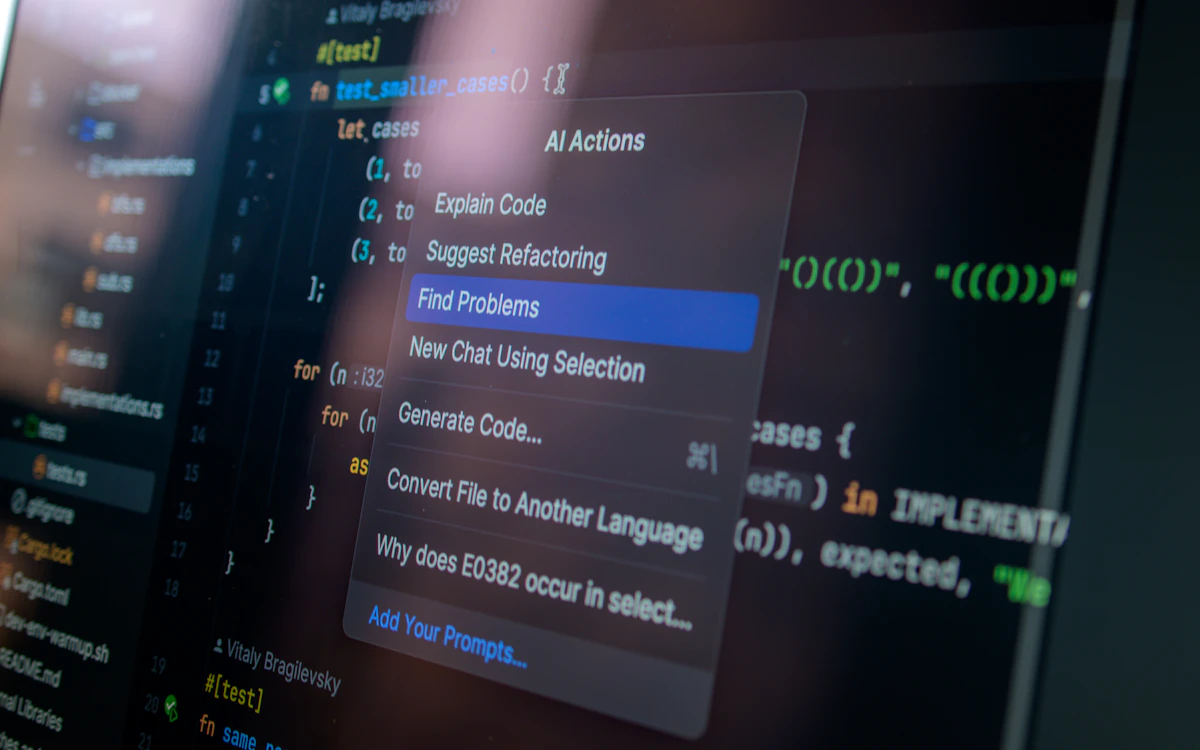
An attacker hijacked an active session of an artificial intelligence coding assistant at an unidentified software as a service provider, and from there propagated the Shai-Hulud malware to nearly 100 internal code repositories, according to The Hacker News report on September 16 based on a Mandiant report.
According to the reconstruction of the incident, the AI coding agent recommended that the developer install a software package that the attacker had previously poisoned, and the developer accepted that recommendation as part of their normal workflow. Once the recommendation was accepted, the attacker used the developer's active session to install a credential theft program through a malicious PyPI package, the official Python package repository.
From that entry point, the Shai-Hulud worm autonomously propagated to approximately 100 code repositories of the affected organization, stealing both secrets stored in those repositories and source code from the company's products. The public report on the case, documented by Mandiant in its September report, does not specify when the intrusion occurred or the exact method the attacker used to take control of the active session of the coding assistant.
The incident confirms a significant change in the attack surface of software development teams: instead of directly compromising the code or credentials of a developer, the attacker exploited the trust that the developer places in the recommendations of their artificial intelligence assistant within their daily workflow.
For engineering teams that already integrate AI coding agents into their workflows, the case confirms the need to treat the recommendations of these assistants with the same scrutiny as any external dependency, rather than automatically accepting them just because they come from a trusted tool.
From the perspective of next+, the hijacking of this AI coding session confirms that the trust placed in AI-assisted development assistants has already become an attack vector in itself, and that no organization can treat the recommendations of these tools as automatically trustworthy without additional verification processes.